Microsoft Data Protection & AI Governance
Lab ID: LAB-MS-001 · Version: 0.3 · Status: Proposed reference design
Purpose of the lab
Explore how identity, device management, data protection, agent administration, and security operations work together to support responsible AI use. The lab emphasizes controlled access to information, visibility into agent configuration and activity, and evidence that supports governance reviews.
Technical architecture
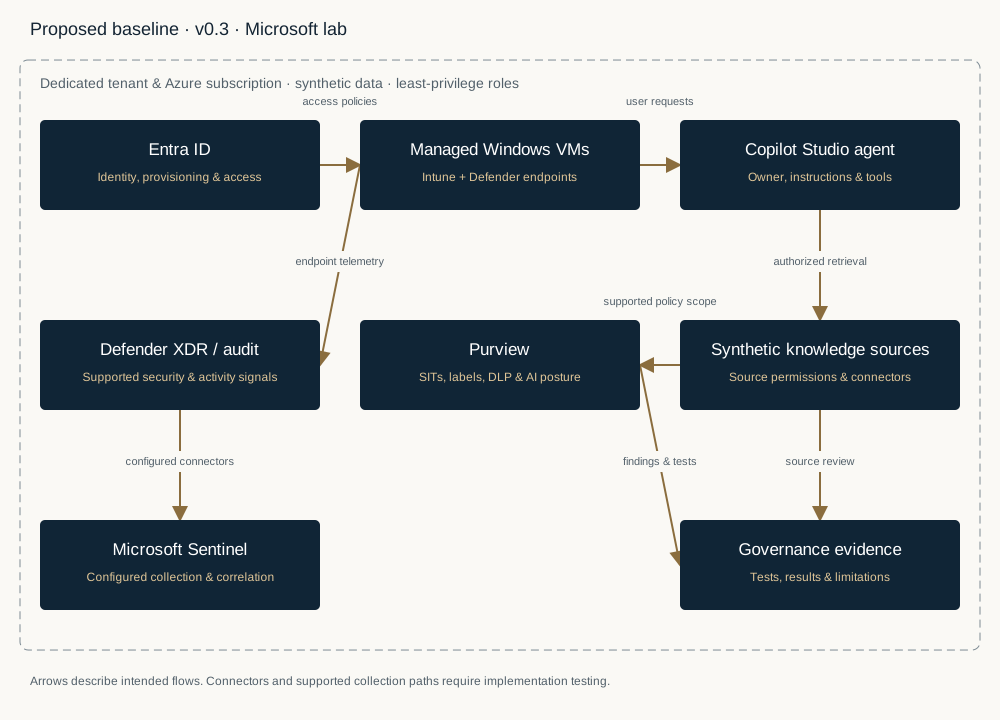
The proposed environment uses a dedicated Microsoft tenant and Azure subscription, test identities, and managed Windows virtual machines. Entra ID governs identity and access; Intune manages endpoints. Synthetic documents and records populate selected knowledge sources. Copilot Studio provides a candidate agent-building environment, with applicable Microsoft administration services used for agent oversight. Purview provides data-protection and AI data-security assessment capabilities where supported. Defender XDR and Sentinel support security investigation and correlation through configured integrations.
These services form a logical reference architecture. Collection paths, supported workloads, permissions, licenses, and feature availability must be confirmed during implementation. A configured knowledge source does not, by itself, prove that its contents were used in a particular response.
Baseline architecture
Components, purpose, and testing opportunities
| Component or feature | Brief description and purpose | Proposed implementation and tests |
|---|---|---|
| Azure administration | Resource and subscription administration provides the operational foundation. | Configure resource groups, budgets, tags, role assignments, diagnostic settings, and environment shutdown procedures. Test administrative access and auditability. S01 ↗ |
| Microsoft Entra ID — provisioning | Identity lifecycle management establishes controlled test accounts and group membership. | Create test users, groups, and supported application identities; test provisioning, role changes, and access removal. S02 ↗ |
| Entra ID — access controls | Authentication and authorization determine who can access resources. | Exercise multifactor authentication, Conditional Access, least-privilege assignments, and supported application or agent permissions. Record allowed and denied outcomes. S03 ↗ |
| Microsoft Intune | Endpoint management applies configurations and evaluates device compliance. | Enroll eligible Windows VMs, deploy policies, and test compliant and noncompliant device scenarios with applicable access controls. S04 ↗ |
| Windows virtual machines | Isolated workstations provide repeatable user and security test environments. | Create documented baselines and recovery procedures; exercise user workflows, endpoint controls, and synthetic sensitive-data handling. S05 ↗ |
| Microsoft Defender XDR | Supported security signals and investigation tools help detect and investigate threats. | Onboard supported endpoints; use benign simulations to assess alerts, investigation context, and response actions. Confirm licensing and integration prerequisites. S06 ↗ |
| Purview sensitive information types — SITs | Pattern- and context-based identification helps recognize sensitive information. | Evaluate supported built-in and custom types against synthetic identifiers, including near-matches and negative examples. Measure missed detections and false positives. S07 ↗ |
| Purview classification and sensitivity labels | Classification identifies data categories; labels communicate sensitivity and can apply protection settings. | Test manual and supported automatic labeling, label persistence, and configured protection behavior. Distinguish discovery results from enforced protection. S08 ↗ |
| Purview Data Loss Prevention — DLP | Policies evaluate supported data-handling activities and can apply protective actions. | Test applicable sharing or transfer scenarios, alerts, policy tips, overrides, and blocks. Document workload coverage and exceptions. S09 ↗ |
| Microsoft Purview Data Security Posture Management for AI — DSPM for AI | Proposed assessment component for identifying data-security risks associated with supported AI usage. | Assess available AI activity discovery, sensitive-data exposure findings, posture assessments, and recommendations. Confirm the current product name, supported agents, data coverage, and evidence available in the tenant. S10 ↗ |
| Microsoft Copilot Studio | Agent authoring and configuration provide a controlled subject for governance exercises. | Build a small reference agent with synthetic knowledge, document instructions and tools, and test publication and access settings. S11 ↗ |
| Agent inventory, registration, and ownership | Applicable agent administration services establish accountability for agents. | Identify the supported registration or inventory mechanism; record agent ID, owner, purpose, environment, publication state, and review date. Test ownership changes and retirement. Registration mechanisms vary by agent type. S12 ↗ |
| Knowledge sources and connectors | Connections define the information and external capabilities available to an agent. | Document SharePoint or other supported sources, authentication mode, permission scope, refresh behavior, and connector configuration. Test authorized retrieval, restricted retrieval, and source removal. S13 ↗ |
| Agent monitoring and audit | Available activity and audit records support operational oversight and investigation. | Evaluate agent usage, administrative changes, tool actions, errors, and available interaction records. Determine what sources can be attributed to a response and where visibility is incomplete. S14 ↗ |
| Microsoft Sentinel | Central security analytics combines supported telemetry for detection and investigation. | Configure appropriate connectors and diagnostic collection; test correlation rules and investigation workflows. Verify actual event arrival rather than assuming all agent activity is collected. S15 ↗ |
| Optional tokenization service | Replaces selected sensitive values with substitute tokens when explicitly implemented. | Evaluate an independent application or service integration, access to reidentification, and accidental disclosure. Tokenization is a separate extension, not an assumed Purview capability. S16 ↗ |
Terminology: Use the full name Microsoft Purview Data Security Posture Management for AI (DSPM for AI) provisionally for the previously discussed “MSDP.” Verify current Microsoft naming before publication. AI token consumption, credential or access tokens, and data tokenization are separate concepts and require separate tests.
Implementation stages, test scenarios & evidence
Implementation stages
1. Establish the tenant, subscription, test accounts, permissions, licensing inventory, and resource budget.
2. Build Windows VMs, enroll supported devices, and configure endpoint management and security collection.
3. Create a synthetic data corpus with known classifications, labels, and access permissions.
4. Configure supported Purview policies and establish baseline detection and enforcement behavior.
5. Build a reference agent; document ownership, registration, knowledge sources, connectors, instructions, and permissions.
6. Enable available monitoring and audit collection; integrate selected signals into Sentinel.
7. Run the test cases and preserve results, limitations, and cleanup steps.
Initial test scenarios and evidence
| Test | Question and expected behavior | Evidence to retain |
|---|---|---|
| MS-01 — Identity lifecycle | Does removing a user’s access prevent subsequent access after applicable propagation and session handling? | Group and role changes, sign-in results, timestamps, and session conditions. |
| MS-02 — Sensitive-data detection | Which synthetic regulated-data patterns are detected or missed? | Labeled test corpus, detector settings, false positives, and false negatives. |
| MS-03 — Protection enforcement | Does a configured policy produce the intended outcome for a supported transfer or sharing action? | Policy version, activity record, user experience, alert, and observed enforcement. |
| MS-04 — Agent accountability | Can an administrator identify the agent, its accountable owner, access scope, and publication state? | Inventory export or review record and lifecycle change history. |
| MS-05 — Knowledge-source boundaries | Does the agent respect the intended authorization model across permitted and restricted sources? | Test identity, authentication configuration, source permissions, prompts, responses, and available citations or logs. |
| MS-06 — Agent actions and monitoring | Are selected agent actions and configuration changes visible in the configured monitoring tools? | Agent and connector configuration, available activity records, timestamps, and telemetry gaps. |
| MS-07 — Security investigation | Can a benign endpoint event be investigated alongside relevant identity or other available telemetry? | Detection, investigation notes, correlation results, and response record. |
| MS-08 — Agent retirement | Does disabling an agent and removing its connections prevent the targeted workflows? | Retirement actions, access attempts, remaining dependencies, and retained audit records. |
Requirements and limits
Use a dedicated test environment and synthetic regulated data. Licensing, preview status, service names, regional availability, and supported telemetry are implementation dependencies. This design does not assert that DSPM for AI alone registers agents or provides complete source-level monitoring. Successful lab tests establish evidence for the tested configuration; they do not establish regulatory compliance.
Microsoft sources
Microsoft product documentation supports the proposed components. Availability, licensing, permissions and agent coverage must be confirmed in the selected tenant. The optional tokenization reference provides general security guidance; it does not describe a built-in Purview tokenization service.
- S01 — Cloud Provider — Azure Foundation · Set up identity in Azure - Cloud Adoption Framework | Microsoft LearnRetrieved 30 October 2026
- S02 — Identity Provisioning · What is automated app user provisioning in Microsoft Entra ID - Microsoft Entra ID | Microsoft LearnRetrieved 30 October 2026
- S03 — Identity & Access Controls · Microsoft Entra Conditional Access: Zero Trust Policy Engine - Microsoft Entra ID | Microsoft LearnRetrieved 30 October 2026
- S04 — Endpoint Management · What is Microsoft Intune? - Microsoft Intune | Microsoft LearnRetrieved 30 October 2026
- S05 — Windows Virtual Machines · Overview of virtual machines in Azure - Azure Virtual Machines | Microsoft LearnRetrieved 30 October 2026
- S06 — Threat Detection & Response — XDR · What is Microsoft Defender XDR? - Microsoft Defender XDR | Microsoft LearnRetrieved 30 October 2026
- S07 — Sensitive Information Identification · Learn about sensitive information types | Microsoft LearnRetrieved 30 October 2026
- S08 — Data Classification & Sensitivity Labels · Learn about sensitivity labels | Microsoft LearnRetrieved 30 October 2026
- S09 — Data Loss Prevention · Learn about data loss prevention | Microsoft LearnRetrieved 30 October 2026
- S10 — AI Data Security & Compliance · Microsoft Purview data security and compliance protections for Microsoft 365 Copilot and other generative AI apps | Microsoft LearnRetrieved 30 October 2026
- S11 — Agent Development — Copilot Studio · Overview - Microsoft Copilot Studio | Microsoft LearnRetrieved 30 October 2026
- S12 — Agent Inventory & Administration · Agent overview in Microsoft 365 admin center | Microsoft LearnRetrieved 30 October 2026
- S13 — Knowledge Sources & Connectors · Knowledge sources summary - Microsoft Copilot Studio | Microsoft LearnRetrieved 30 October 2026
- S14 — Agent Analytics & Monitoring · Monitor agent performance in Copilot Studio - Microsoft Copilot Studio | Microsoft LearnRetrieved 30 October 2026
- S15 — Security Analytics — SIEM · What is Microsoft Sentinel SIEM? | Microsoft LearnRetrieved 30 October 2026
- S16 — Optional Tokenization — Supporting Security Guidance · Cryptographic Storage - OWASP Cheat Sheet SeriesRetrieved 30 October 2026